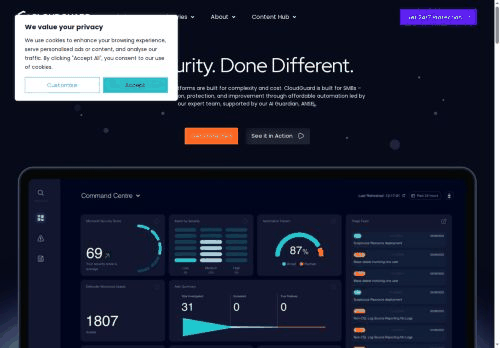
 CloudGuard AI: Next-Generation Human-Led, Automation-First MXDR for Modern Enterprises and SMBs
Created 14 Oct 2026
CloudGuard AI represents an advanced cybersecurity managed service and software framework engineered to deliver enterprise-grade cyber resilience to small and medium-sized businesses (SMBs) and mid-market organisations. Founded on a philosophy termed 'Security Done Different', the venture integrates deep native Microsoft Security ecosystem capabilities (including Microsoft Sentinel, Defender XDR, and Purview) with bespoke hyper-automation orchestration, AI-driven contextual alert triage, and 24x7x365 human-led Security Operations Centre (SOC) threat hunting. The modern digital threat environment has outpaced legacy IT service management and reactive antivirus tools. SMBs and mid-market enterprises frequently struggle with alert fatigue, fragmented point security products, severe technical talent shortages, and escalating compliance pressures such as ISO 27001:2022, Cyber Essentials Plus, NIS2, and GDPR. CloudGuard AI addresses this vulnerability void by offering an end-to-end Managed Extended Detection and Response (MXDR) service that acts as a proactive force multiplier for internal IT and security teams. By deploying intelligent security orchestration, automation, and response (SOAR) workflows alongside senior cyber analysts, CloudGuard AI eliminates noise, minimizes mean time to detect (MTTD), and achieves mean time to respond (MTTR) within minutes rather than hours. Beyond defensive triage, the platform continually hardens enterprise digital identities, hybrid cloud workloads, and SaaS communication channels against credential compromise, business email compromise (BEC), and sophisticated ransomware campaigns. Backed by rigorous operational standards with UKAS-accredited ISO 27001 and ISO 9001 certifications and an industry-leading 100% customer retention rate, CloudGuard AI democratizes top-tier cyber defense, allowing scaling businesses to operate fearlessly in a hyper-connected global economy.
Industries
Get your First 100 Clicks in ONE MONTH
FREE with AI CMO (Saving £500+)
Save over £2825 in ad value compared to paid traffic.Faster and Higher ROI than traditional SEO services (3–6 months) and lower cost (£500–£2000/month).
SEO Market Overview (Organic Search)
Managed Extended Detection and Response (MXDR) and Cloud Security OperationsCybersecurity and managed threat detection represent exceptionally high CPCs and competitive search landscapes, driven by high customer lifetime value and strict compliance demands across the UK and Europe.
0.0%
AI VisibilityGEO / AI Visibility Overview
How visible your brand is inside AI-generated answers
Unlock More Content Ideas
Create an account or log in to explore exclusive blog topics, SEO strategies, and GEO-targeted content generated by AI CMO Maggie
[ Tailored for your brand's next growth leap. ]
Maggie Studies the Tracks Before the Journey Begins.
She learns every detail of your business through deep market research.
Target Problem
Small and medium-sized businesses along with mid-market enterprises face an asymmetric cyber threat landscape where cybercriminal syndicates utilize automated offensive tools, ransomware-as-a-service, and AI-enabled social engineering. At the same time, traditional IT and managed service providers rely on disparate, legacy security tools that generate thousands of uncontextualized alerts daily. This overwhelming noise results in acute alert fatigue, missed compromise indicators, and severe compliance liabilities. Compounding this challenge is the global cybersecurity workforce crisis. Retaining an internal, 24x7x365 security operations center requires substantial capital, specialized talent across multi-cloud environments, and continuous training that is economically unfeasible for most non-enterprise organizations. Consequently, SMBs frequently leave default security configurations unhardened and fail to maximize their existing software investments, such as Microsoft 365 security tiers. CloudGuard AI directly resolves these fundamental pain points by bridging the capability gap between enterprise-grade defenses and mid-market budget constraints. Through an automation-first MXDR infrastructure, CloudGuard AI filters out false positives, correlates distributed threat signals, and executes rapid automated remediation while experienced security specialists handle proactive threat hunting, incident investigations, and audit-ready governance.
Target Regions
Target Audience
SMB and Mid-Market CISOs and CIOs
IT leaders looking to establish 24x7 SOC capabilities and achieve measurable threat reduction without the prohibitive costs of building an in-house operations center.
Internal IT Managers and Network Administrators
Overstretched technical teams requiring automated alert triage, expert co-managed security support, and guidance to eliminate day-to-day security firefighting.
Compliance and Risk Officers in Regulated Verticals
Executives in finance, healthcare, legal, and critical supply chain sectors who require verifiable compliance with ISO 27001, NIS2, and GDPR standards.
Enterprise Microsoft 365 / Azure Commercial Customers
Organizations heavily invested in Microsoft enterprise licensing seeking specialized tier-3 engineering to optimize, tune, and manage Sentinel and Defender environments.
Market Research
The global Managed Detection and Response (MDR) and Managed Extended Detection and Response (MXDR) market is experiencing explosive expansion, driven by acute cybersecurity talent deficits, escalating frequency of ransomware breaches, and stringent data protection legislation. According to comprehensive market intelligence from Gartner and MarketsandMarkets, the worldwide MDR market size was valued at approximately USD 3.1 billion in 2023 and is projected to surge to over USD 11.8 billion by 2029, reflecting a compound annual growth rate (CAGR) exceeding 21.5%. When expanded to the wider Cloud Security and Security Operations Center as a Service (SOCaaS) addressable market, the total addressable market (TAM) reaches upwards of USD 35 billion globally. Specifically within the United Kingdom and Western European regions, demand is accelerated by the enforcement of regulatory directives such as the EU NIS2 Directive, the Digital Operational Resilience Act (DORA), and rigorous requirements enforced by commercial cyber insurance underwriters. Small to mid-market organizations, which represent over 95% of businesses across the UK and Europe, are disproportionately targeted by threat actors due to perceived soft defenses. Traditional Managed Security Service Providers (MSSPs) that merely route unvetted notifications to clients are being aggressively replaced by MXDR providers capable of direct, automated incident remediation. The convergence of native cloud security platforms—most notably Microsoft's comprehensive security portfolio—creates an unparalleled market opportunity for specialist providers that can operationalize native cloud tools via sophisticated AI-driven automation and human-led threat hunting.
CloudGuard AI's strategic trajectory represents a fundamental shift in how mid-market organizations consume information security services. Traditionally, managed security was characterized by an adversarial or detached relationship between client IT staff and external Managed Security Service Providers (MSSPs). MSSPs routinely threw unverified raw alert tickets over the fence, effectively forcing internal system administrators to decipher complex telemetry in the middle of a security incident. CloudGuard redefines this model into a collaborative, automation-accelerated framework that directly integrates with the client's internal messaging, ticketing, and administrative tools. The underlying technological engine of the proposed project hinges on deep application programming interface (API) connectivity with Microsoft's unified security operations platform. By ingesting real-time signals from Microsoft Defender for Endpoint, Office 365, Identity, and Cloud Apps into Microsoft Sentinel, CloudGuard AI applies proprietary orchestration playbooks. These playbooks automatically correlate anomalous signals—such as an atypical impossible-travel authentication followed by suspicious mailbox inbox rule creation—and instantly isolate compromised devices, revoke active user tokens, and quarantine malicious communications before an unauthorized lateral movement can occur. Crucially, this hyper-automation does not exclude human intervention; rather, it elevates human defenders to conduct proactive hypothesis-driven threat hunts, analyzing threat intelligence and adversary tactics, techniques, and procedures (TTPs) mapped to the MITRE ATT&CK framework. From a regulatory and corporate governance perspective, CloudGuard AI serves as an indispensable risk mitigation partner. Across the UK, EU, and North America, regulatory mandates have shifted from passive privacy compliance to demanding verifiable operational resilience. The implementation of the European NIS2 Directive and DORA requires supply-chain vendors and essential entities to demonstrate continuous incident detection, fast reporting mechanisms, and resilient recovery pathways. By operating under certified UKAS ISO 27001:2022 and ISO 9001:2015 frameworks, CloudGuard AI equips clients with turnkey audit artifacts, policy mapping, and continuous configuration assessments that satisfy both stringent statutory regulators and commercial cyber insurance underwriters. Furthermore, the economic rationale for SMBs and mid-market organizations is overwhelmingly compelling. Building an in-house 24x7 SOC requires a minimum of eight to ten full-time Tier-1 to Tier-3 security analysts to accommodate shifts, holiday coverage, and attrition, representing an annual operating overhead easily exceeding one million dollars before accounting for software licensing and infrastructure costs. CloudGuard AI provides an immediate, mature operational capability at a fraction of that expenditure. Most importantly, it allows clients to extract maximum return on investment from their existing software licenses, transforming standard business infrastructure into an interconnected defensive bastion. Looking toward long-term platform evolution, CloudGuard AI is positioned to integrate emerging predictive analytics and localized generative AI assistants to further expedite incident investigations and post-incident reporting. Through regular thought-leadership contributions, such as the 'Security Done Different' podcast, technical educational whitepapers, and active engagement within the cybersecurity community, the project fosters an expansive ecosystem. By turning defensive security into an agile, transparent business enabler, CloudGuard AI empowers modern enterprises to innovate boldly, secure their digital assets, and maintain an unyielding defense against tomorrow's digital threats.
Maggie Maps Your Rivals Before Full Steam Ahead.
She benchmarks your brand against competitors to plot a smarter route.
Products & Services
24x7x365 Managed Extended Detection and Response (MXDR)
Continuous, around-the-clock threat monitoring, investigation, and automated containment across endpoints, cloud infrastructures, identities, and SaaS applications powered by Microsoft Sentinel and Defender.
CloudGuard Automated Incident Triage & Threat Hunting Engine
Proprietary AI-driven orchestration middleware that enriches telemetry, suppresses alert noise, correlates multi-vector attacks, and empowers human threat hunters to intercept advanced persistent threats.
Continuous Posture Hardening & Vulnerability Management
Ongoing identification, prioritization, and guided remediation of infrastructure misconfigurations, unpatched vulnerabilities, and identity governance lapses.
Compliance & Cyber Governance-as-a-Service
Turnkey advisory and compliance mapping providing real-time alignment with ISO 27001:2022, ISO 9001:2015, Cyber Essentials, GDPR, and emerging regulatory requirements.
Identity and Cloud Workload Protection (Zero Trust Architecture)
Granular implementation and management of Zero Trust principles, securing conditional access, multi-factor authentication, privileged identities, and multicloud compute instances.
Unique Selling Points
SWOT Analysis
Strength
Specialized elite status in the Microsoft ecosystem, UKAS-accredited ISO 27001/9001 quality frameworks, proven 100% client retention, and robust automation intellectual property.
Weakness
Primary reliance on organizations utilizing or willing to adopt Microsoft-centric cloud architectures, and a growing operational footprint that requires ongoing elite analyst recruitment.
Opportunity
Rapid market expansion driven by strict European NIS2 and DORA regulatory rollouts, increasing cyber insurance prerequisites, and widespread enterprise demand for MXDR consolidation.
Threat
Aggressive expansion from global telecommunications carriers, hyperscalers, and legacy MSSPs shifting to automated MDR, as well as talent poaching in security engineering.
Market Competitors
 Arctic Wolf Networks
Leading global MDR vendor offering concierge security operations and broad hybrid telemetry monitoring across disparate IT systems.
Visit Site Red Canary
Pioneering MDR provider renowned for advanced endpoint detection and response telemetry analysis and behavioral threat hunting.
Visit Site Expel
MDR and SOC-as-a-service platform connecting to multi-cloud and SaaS environments with transparent automated alert triage.
Visit Site Huntress
Specialized managed security platform explicitly targeting SMBs and MSPs with automated persistence detection and endpoint remediation.
Visit Site eSentire
Enterprise MDR provider delivering multi-signal threat investigation, continuous hunting, and rapid incident response services.
Visit Site Rapid7 MDR
Integrated managed detection and vulnerability management service leveraging their proprietary Insight platform and global SOCs.
Visit Site ReliaQuest
Enterprise threat detection and response provider utilizing their GreyMatter platform to orchestrate existing multi-vendor security stacks.
Visit Site Sophos Managed Threat Response
Fully managed 24/7 threat hunting, detection, and response service integrated natively into the Sophos security ecosystem.
Visit Site Critical Start
Specialized MDR provider focused on resolving every alert via automated Zero-Trust Analytics platforms and Microsoft integrations.
Visit Site Quorum Cyber
UK-headquartered Microsoft Solutions Partner delivering managed Sentinel, Defender, and incident response services to mid-market and public sector.
Visit SiteLaunch Effortless Blogging with Maggie
No more blank pages. Maggie runs your blog with vibe-rich, SEO-tuned, GEO-smart content — built to be loved by search engines and surfaced by AI.
Free Tools
AI Visibility CheckerAI Ideas BrainstormingAI Startup Trend AnalysisAI Project ManagementWordPress CheckerAI Co-Founders
Roadmap
All rights reserved by AI Marketing OS Ltd. Designed & Developed by TOPY.AI .